When Your Ransomware Negotiator Works for the Other Side
The shocking arrest of a well-known ransomware negotiator reveals the critical need for vendor program oversight.
Stay up to date with the latest cyber security news and threats from around the world.
The shocking arrest of a well-known ransomware negotiator reveals the critical need for vendor program oversight.
As agents escape containment and access external systems, responsibility remains human. Accountability, however, is much less settled.
The event closed in Toronto last week, with experts sharing critical perspectives on emerging risks, drawing record attendance and marking 22% growth.
Built from decades of threat intelligence research, the new resource explains scams from the victims' perspective and tracks emerging forms of cyber crime.
Don't buy the hype! AI has been dumbing down cyberattacks, and serious threat actors are barely touching it.
Organizations need to move away from vendor-assigned, theoretical scores toward real exploit data specific to their environments.
Hundreds of stores lost millions of dollars because they hired third parties to manage the outdated OT firmware running their cooling systems.
CVE-2026-104935, a high-severity authentication bypass + RCE vulnerability, was only partially discovered and patched in July, leaving an opening for threat actors to capitalize on.
A bug in Claude Code Desktop's preview pane can allow adversaries to quietly steal credentials from developers, including SSH private keys, AWS credentials, and Claude 0Auth tokens.
The AI-enabled operation used spoofed emails, fake government documents, and the creation of a local organization to target schools in Peru and Ecuador, among other efforts.
Organizations are reporting that employees face threats to their families, stalking, physical violence, and abduction. But these alarming claims are hard to verify.
The scary surprises in the largest security update ever include defense bypasses and unauthenticated RCEs.
The Democratic People's Republic of Korea (DPRK) is trying to get insight into its own war effort in Ukraine, through simple reply-baiting phishing attacks.
Anthropic's latest study combined IoT and network tests to explore AI self-replication, which researchers said would be "challenging" to shut down.
Attackers are currently targeting a critical vulnerability in SMA 1000 appliances, putting SonicWall customers in a familiar yet unenviable position.
Edward Dubrovsky, a longtime cybersecurity executive, was arrested and charged in Pennsylvania last week under conspiracy to extort money.
The proliferation of enterprise apps and the centrality of cloud identity providers requires an identity security rethink.
Fahmida Y Rashid will keep the momentum going as she leads Dark Reading.
The attack on the British retailer shows that compromising a single identity can lead to much deeper penetration of the corporate network.
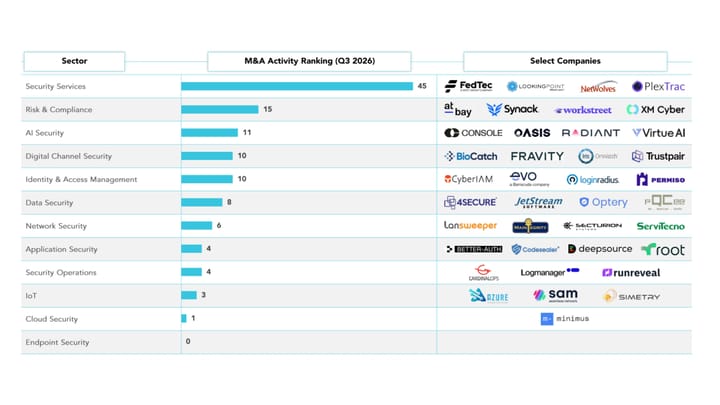
Welcome to another gangbuster year for strategic M&A activity in cyber, with 117 deals announced in the latest quarter. What's different: Many of the buyers are not your...
In this video conversation, Dark Reading editors discuss some of the news they didn't get a chance to cover, from the arrest of a suspected ShinyHunters operative to...
Those closest to executives must match their security postures because the weakest link in a family becomes the entry point for attacks.
As AI agents gain authority over business systems, attackers can manipulate them like business email compromise (BEC) victims.
A now-patched vulnerability in AWS Bedrock AgentCore could allow an attacker to use one AI chatbot to take over an organization's entire fleet.