EU Grocers Pay a Steep Price for Unpatched Fridge Firmware
Hundreds of stores lost millions of dollars because they hired third parties to manage the outdated OT firmware running their cooling systems.
Hundreds of stores lost millions of dollars because they hired third parties to manage the outdated OT firmware running their cooling systems.
Hundreds of French grocers likely lost many millions of dollars this week from cyberattacks that manipulated their refrigeration systems.
Overnight on Monday, hackers broke into commercial refrigeration system controllers at major French grocery chains. They converted refrigerators, freezers, and cold storage rooms into heating units, raising their temperatures up to 50 degrees Celsius (over 120 degrees Fahrenheit), completely spoiling all of the food they contained, and reportedly even causing some small fires. The threat actor’s identity and motives are unclear.
Refrigeration controllers allow grocers to set and monitor their fridge temperatures remotely, 24/7. It follows, then, that store owners could’ve been alerted to, or manually discovered, the fact that something was amiss. To prevent that from happening, French sources report that the attackers extended their targeted systems’ defrost cycles — where freezers intentionally melt accumulated frost and ice — so that the heating looked like routine maintenance.
According to the companies’ own reports, the attacks impacted somewhere north of 400 grocery and retail stores, all on the same night. An analyst for French cybersecurity company Sekoia told Reuters that Spain, Portugal, Poland, Germany, and Belgium had also been affected.
Just two supermarkets in the Alsace region reported combined losses of 270,000 euros (about $300,000 USD), according to the BBC. If those two cases are anything to go by, losses for all 400 stores could total many, many millions of euros.
Worst of all, experts point out that the attacks were almost certainly avoidable with standard cyber hygiene.
What Caused Freezers to Burn?
Initial reports suggested that Monday’s attacks traced back to refrigeration controllers from Danish manufacturer Danfoss. Danfoss has a large footprint in supermarket and food retail control solutions, with more than 50,000 installations of its technology worldwide, according to its website.
On Aug. 9, cybersecurity researchers from Claroty’s Team82 disclosed three vulnerabilities in Danfoss’ AK-SM 800A platform. The issues — assigned CVE-2025-41450, CVE-2025-41451, and CVE-2025-41452 — allowed attackers to perform remote code execution (RCE) or denial-of-service (DoS) against enterprise refrigeration fleets. Danfoss patched the vulnerabilities but counted on customers to update their systems themselves.
In a statement to Reuters, Danfoss pinned the blame on customers running outdated firmware, writing that it “long advised customers to keep supported systems updated with the latest firmware and to migrate legacy systems to current-generation solutions.”
The original equipment manufacturer (OEM) provided more information to a refrigeration news publication, Cooling Post. The “majority” of affected units, it said, were running AK-SM 800 or its older AK-SC355. Both systems are long since end of life: the former as of 2021, the latter 2016.
By Tuesday, France’s national CERT (CERT-FR) had identified that another refrigeration controller platform — “XWEB,” from vendors Dixell and parent company Copeland — had also been involved in the attacks. It didn’t specify what vulnerabilities or firmware versions might’ve been at fault, though the circumstantial evidence now surely points to threat actors building off of Team82’s research. On the exact same day they outed those vulnerabilities affecting Danfoss, the same researchers disclosed 23 affecting XWEB Pro, 21 of high severity.
Grocers Were Warned on Possible Fridge Attacks
On Aug. 26, a strange collection of similar reports started to seep out of US military installations.
Refrigeration units were dying. In each base where it was happening, folks probably figured they were dealing with some odd electrical issue. But then more and more stations reported the same thing.
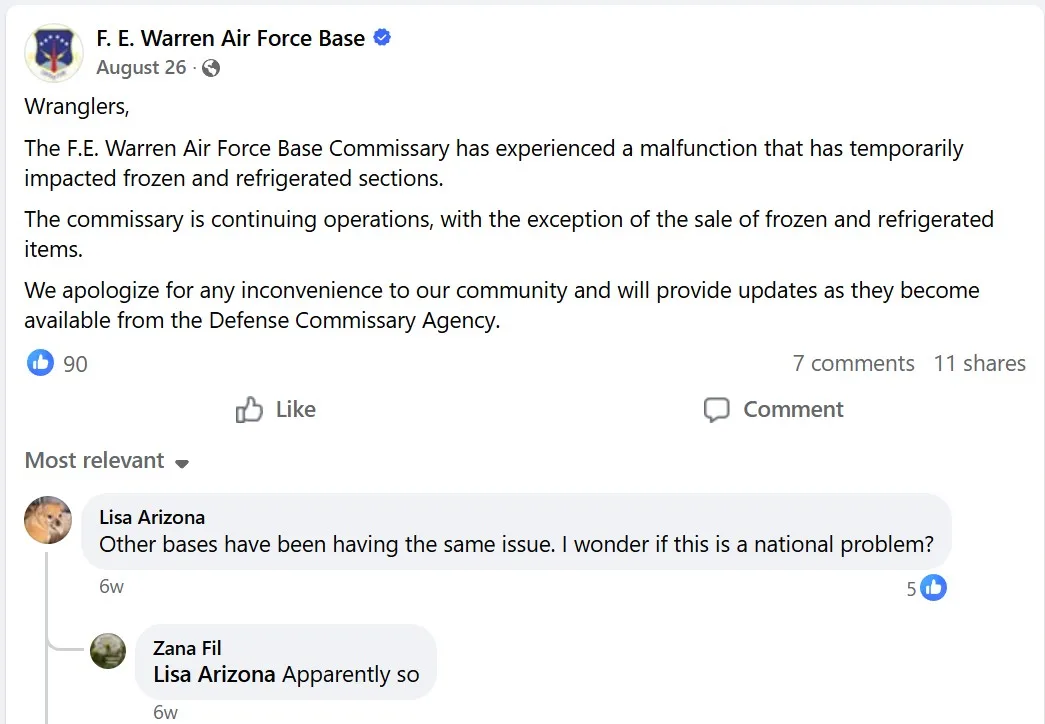
Source: F. E. Warren Air Force Base via Facebook
After coming across these odd reports on social media, an independent journalist took a wild guess. “Self-aware enough to know this sounds insane, but I need you to stick with me,” wrote M. Elizabeth on Substack. “I think there is a nonzero chance someone has hacked the commissary freezers.”
To date, the US military has not confirmed who or what caused outages at commissaries spread across at least 14 separate Air Force bases, Navy installations, and Army posts. It could have been a coincidence that the attacks occurred only two weeks after Danfoss’s vulnerability disclosures.
It would be extra coincidental considering that the Defense Commissary Agency (DeCA) — the Defense Department’s (DoD) central agency overseeing military commissaries — has explicitly referenced working with Danfoss technologies in the past. For example, in a template technical specification for commissary contractors from June 2022, DeCA referenced the Danfoss AK-SM 800A as a “basis for design” for individual control units.
Beware, Grocers Everywhere
In his own experience, Xona Systems CEO Bill Moore recalls, “At a lot of these stores that are brick-and-mortar retail — but also manufacturing plants, power plants, oil and gas sites, it’s across the board — the biggest problem out there is that organizations do a pretty good job at segmenting their own networks. But when it comes to OT, there are all of these OEMs and third parties that need access. And organizations have not really paid attention.”
By granting many vendors and OEMs access to their systems, organizations end up exposing themselves to remote attacks. “And there’s literally no visibility or governance over a lot of those connections. I would say it’s true in a big percentage of cases — half, maybe more, across the board. They let all of their OEMs kind of do their own thing, but then we’ve seen a lot of hackers compromise those third-party connections,” he laments.
In an email to CNBC, Les Mousquetaires — parent company to Intermarché and Netto — explained that its attack occurred via a service provider in charge of refrigeration systems in some of its stores.
“Bottom line: take your gear off the Internet,” says Andrew Ginter, vice president of industrial security at Waterfall Security Solutions. Shodan searches this week yielded thousands of Internet-exposed Danfoss systems, for example, with around 1,500 in France alone.
In a perfect world, organizations would protect their control systems behind hardware-enforced remote access, Ginter says, “but even a humble firewall between these devices and the Internet would help.”
For basic firewalls, he advises that organizations:
-
Put a “deny all” rule in
-
Allow connections from only specific IP addresses
-
Apply a password and two-factor identification to those connections
-
Auto-update the firewall, to avoid forgetting
-
Use commercial-grade or industrial-grade devices, not consumer-grade; many consumer-grade devices do not provide updates, or do not update at all promptly
Finally, he adds, “Replace the firewall strictly every four years. Why? Because if we have Internet-exposed devices, nine times out of 10 we don’t have a security team, and we’re not going to notice when our firewalls go out of support and auto updates stop.”
“The very basics are not enough for big-iron critical infrastructure or heavy industry, but they’ll go a long way toward keeping hacktivists out of your freezers,” Ginter concludes. “Get your stuff off the Internet. Do it on an emergency basis.”
Read more about: