Malicious ScreenConnect deployments observed
Categories: Threat ResearchTags: advisory, connectwise, ScreenConnect
Stay up to date with the latest cyber security news and threats from around the world.
Categories: Threat ResearchTags: advisory, connectwise, ScreenConnect
Categories: Threat ResearchTags: advisory, N-able
<p>An agentic AI pentesting framework is being used in the wild by threat actors</p>Categories: Threat ResearchTags: Agentic AI, Attack Tools, AI
The GOLD OGRE threat group has used AI extensively to develop tools and to orchestrate and execute ransomware operationsCategories: Threat ResearchTags: AI, Ransomware, Aur0ra
Categories: Threat ResearchTags: advisory, vulnerability, Node2Shell, Brotli
<p>The China-based threat group uses DLL sideloading in these attacks</p>Categories: Threat ResearchTags: BRONZE SANDCASTLE, Meterpreter, Sandboxie
No novelty required to be effectiveCategories: Threat Research, X-ops, Sophos SecOpsTags: incident response
<p>Automated sign-ins used the vendor's Entra application identity to request Microsoft Graph tokens across consenting tenants</p>Categories: Threat ResearchTags: connectwise
<p>This article was first published <a href="https://www.linkedin.com/pulse/building-intent-based-access-control-without-reading-minds-borges-dxg6e/" target="_self">on LinkedIn</a>.</p>Categories: AI Research, Threat ResearchTags: AI, AI RESEARCH, Threat Research
Categories: Threat ResearchTags: advisory, vulnerability, Citrix
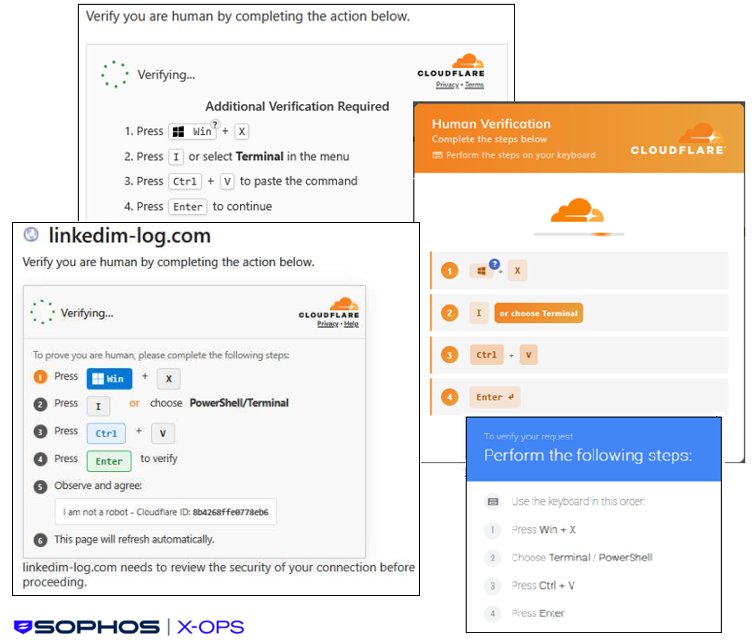
The activity is linked to a broader campaign that previously used a different delivery mechanismCategories: Threat ResearchTags: TerminalFix, clickfix, Lorem Ipsum Loader
Categories: Threat ResearchTags: advisory, vulnerability, Citrix
Categories: Threat ResearchTags: advisory, Kiteworks