The Closed Quorum: Inside the first reported autonomous AI C2 implant
CLOSEDQUORUM, a malware binary discovered through Cisco Talos’ CAIRN project, exhibits fully autonomous command and control (C2). While we do...
CLOSEDQUORUM, a malware binary discovered through Cisco Talos’ CAIRN project, exhibits fully autonomous command and control (C2). While we do...
A cairn is a marker left behind on a trail, a deliberately placed stack of stones that helps hikers find...
Executive Summary This article explores how AWS mitigates the security risks associated with publicly exposed Identity and Access Management (IAM)...
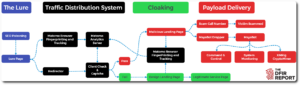
Key TakeawaysIn March 2026, a widespread SEO Poisoning campaign leading to malware deployment and tech support scams was identified by...
Key TakeawaysIn July 2025, BumbleBee malware was deployed via SEO poisoning through a trojanized installer for ManageEngine OpManager.Following initial access,...
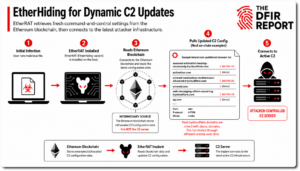
BackgroundThe EtherRAT malware family was first reported by Sysdig back in December 2025. At that time, the initial access vector...
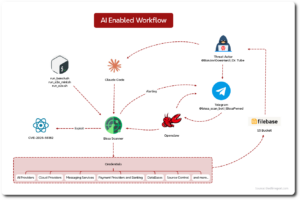
Key Takeaways We recently discovered an exposed server that was used for multi-victim exploitation, staging, review, and validation. Claude Code...
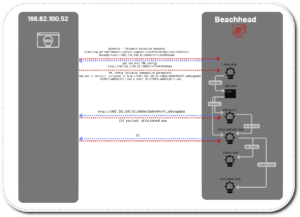
Key Takeaways A threat actor exploited CVE-2023-46604 on an internet-facing Apache ActiveMQ server. Despite being evicted after the initial intrusion,...
Key TakeawaysThe intrusion began with a successful RDP login using already-compromised credentials, likely obtained via an infostealer, data breach reuse,...