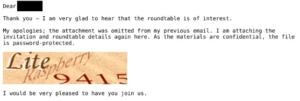
Star Blizzard refines phishing and malware delivery with the RedFlick technique
Since January 2026, Microsoft has observed Russian state threat actor Star Blizzard evolve their detection evasion capabilities through large-scale phishing...
Since January 2026, Microsoft has observed Russian state threat actor Star Blizzard evolve their detection evasion capabilities through large-scale phishing...
Executive Summary Kubernetes operators are coded to drastically reduce operational toil by acting as automated site reliability engineers. However, their...
Attackers are using greater sophistication to gain access to high-yield targets like executives, and company-wide security measures can easily miss...
Microsoft Threat Intelligence has identified NeedyMantis, a modular post-compromise malware family observed in a limited number of targeted operations affecting...
On September 27, 2026, Citrix disclosed eight vulnerabilities affecting NetScaler Application Delivery Controller (ADC) and NetScaler Gateway. Two of these...
We interviewed three Unit 42 consultants to examine the most critical cybersecurity misconceptions observed in their casework across customer environments,...
Threat ResearchadvisoryKiteworksOn September 25, 2026, reports emerged that Kiteworks (formerly Acellion) emailed customers that law enforcement alerted them about an...
Welcome to this week’s edition of the Threat Source newsletter. In the cybersecurity industry, trust is the invisible currency. Every practitioner...
Two UN reports that the Citizen Lab submitted recommendations to have been published this month. One report, from the UN...
Date Published September 22, 2026 Topics Digital Transnational Repression surveillance, transnational repression Mentions Emile Dirks <!-- Senior Research Associate -->...