Why Europe’s Freezer Hacks Spread So Far, So Fast
Europe’s supermarket freezer hacks show how security issues can cascade across an industry, disrupting supply chains at scale.
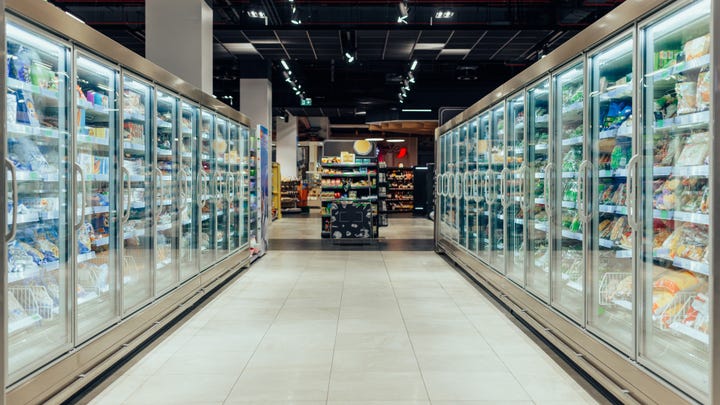
Europe’s supermarket freezer hacks show how security issues can cascade across an industry, disrupting supply chains at scale.
The recent refrigerator hacks wreaking havoc across European supermarkets is a lesson in how shared weaknesses in operational technology (OT) can spread across a whole supply chain.
On the night of Oct. 11, an unknown attacker reportedly compromised refrigeration controls used by hundreds of French supermarkets, triggering extended defrost cycles in refrigerators and freezers across the country. The incident caused millions of euros in damage across roughly 700 impacted stores in France alone, spoiling food, damaging equipment, and even reportedly starting some fires in the process.
The technology leveraged in these attacks included Danfoss refrigeration controllers, as well as Dixell and Copeland XWEB systems. It’s unclear how the threat actor gained access to these systems.
However, the Danfoss controllers at the center of this campaign ran Internet-accessible Web servers. Many were accessible using default login credentials: “admin” as the username and the current date as the password. CERT-FR made a number of recommendations in an advisory to affected supermarkets, such as changing default passwords, factory resetting compromised equipment, and updating firmware. Though to that last point, Danfoss told AFP that many of the attacks involved legacy products that no longer receive updates.
Shared Infrastructure, Big Consequences
What stands out about the French supermarket attacks is how a shared weakness in refrigeration infrastructure appears to have enabled disruption across hundreds of stores. While investigators have not publicly confirmed the initial access vector, the incident raises questions about the risks created when organizations rely on similar technologies, deployment models, and remote-access practices.
Chris St. Myers, director of SentinelLABS, says evidence suggests a common exposure problem, rather than market concentration, may have facilitated this issue.
“CERT-FR confirmed that the French compromises involved Danfoss AK-SM and AK-SC controllers, along with Copeland and Dixell XWEB systems. These technologies are deployed across many retail environments, often with similar remote access requirements and configurations,” St. Meyers says. “That creates opportunities for attackers to reuse the same techniques across otherwise unrelated organizations.”
Thomas Plank, CEO of industrial security firm Tributech, similarly diagnosed common exposure as a core issue behind the attacks.
“What’s concentrated is the setup. Across chains and countries, it’s the same model: remote-management controllers reachable from the internet, often on out-of-support firmware, maintained by a small number of contractors who look after hundreds of stores from one place,” Plank tells Dark Reading. “When everyone runs the same risky pattern through the same few channels, one way in reaches many retailers at once, across borders, overnight. That’s why this looks like a campaign rather than a string of unlucky stores.”
Fridge Attacks Offer Familiar Lessons
It’s highly unusual and hardly precedented for a cyberattack to have such a significant impact on the food supply chain, but it’s not the only incident like it in recent memory.
A similar attack hit refrigeration and freezer systems in stores across other countries at the beginning of November, including Belgium, Estonia, Germany, Ireland, Luxembourg, Netherlands, Poland, Portugal, Spain, and Sweden. Around the same time, attackers targeted the refrigeration of three blood banks operated by the national French Blood Establishment, though the attack was stopped before blood plasma was damaged.
For as alarming and impactful these incidents may seem, supply chain targeting has become more common in recent years with 2021’s Colonial Pipeline attack, Iran’s recent targeting of fuel monitoring systems around the US, and 2024’s Change Healthcare incident.
The danger is clear, especially in the context of a supermarket. Piotr Buliński, chief technology officer (CTO) of Internet of Things (IoT) device management firm Qbee, says a supermarket chain runs thousands of small, unattended OT systems between refrigeration, HVAC, and building management. “Each one is ‘just a few controllers,’ so nobody treats them as critical infrastructure,” he says. “Yet when they fail, the damage is immediate and physical.”
The Perils of Securing OT
These incidents remind us once again about the importance of securing critical infrastructure.
Updating OT systems is a challenging task in their own right because of the downtime often required. Much of the critical technology holding up industrial processes is intended to operate for years (if not decades) on end, while the organizations relying on OT can often include those too under-resourced to have dedicated security staff, like municipalities, or indeed, supermarkets.
Even as these problems have gotten a little easier to address over the years and many dedicated firms have risen to address these challenges, organizations still struggle to secure OT.
St. Meyers believes retail OT has historically received less security attention than traditional industrial environments, despite carrying many of the same underlying risks. He says this is possibly in part because refrigeration, HVAC, and building management systems are “often deployed and maintained outside the traditional IT security organization,” despite being OT.
Plank agrees. He says one solution for retailers is to verify commands at the device level against engineering limits, as “no freezer should ever accept a command to go to 50°C, whoever sends it and whatever channel it arrives on,” referencing the extreme temperatures some targeted equipment reached during the attacks.
For organizations outside the sphere of influence that want to learn from what happened here, there are several lessons: Don’t use default passwords, take inventory of where and how industrial technologies are internet accessible, remove internet exposure wherever possible, and make sure all points of access are secured.
Rafe Pilling, senior director of threat research at Sophos, tells Dark Reading that generally, this incident should be seen as a warning to retailers. “Industrial systems, from energy production to water management to food refrigeration, must be secured, and at a minimum not accessible to malicious hackers via the Internet,” he says.