State Bank of India Suffers a Customer PII Data Leak
Relatively small data breaches in India can turn quite serious, thanks to a sophisticated underground market for trading PII.
Relatively small data breaches in India can turn quite serious, thanks to a sophisticated underground market for trading PII.
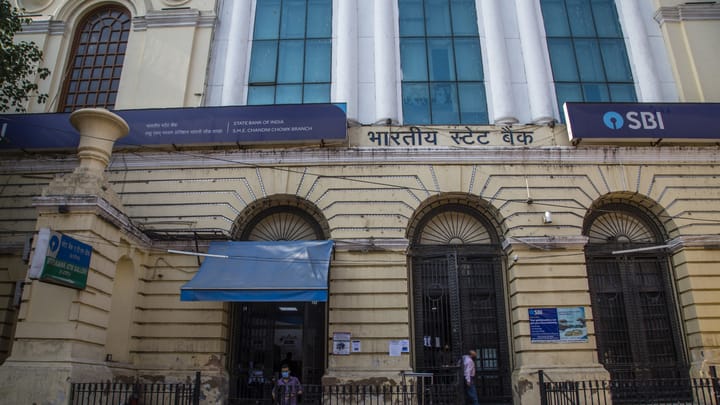
An anonymous hacker has leaked a small batch of sensitive customer records from the State Bank of India (SBI), with potentially serious consequences for the thousands impacted.
SBI has been posting a lot about cybersecurity on social media lately. In August it introduced a new CGI mascot named “Captain Y.” Captain Y from SBI is “your Cyber Protector,” he says in his promo video, “with awareness as his superpower.” SBI’s best plug for cybersecurity awareness came on Wednesday, though, when it publicly disclosed that it had suffered a breach of customer data.
In a notice to India’s National Stock Exchange, the organization’s compliance and company secretary acknowledged that 3,897 customer records had been leaked online. They did not specify whether those records belonged to 3,897 individual customers. In a public notice to customers, the state-run bank emphasized that the incident really only impacted “a very, very small number of customers.”
For a bank that serves north of 500 million people, a few thousand records does indeed qualify as very, very small. Cyber experts note, though, that for those affected, the consequences could be significant thanks to India’s sophisticated underground economy for buying and selling personally identifying information (PII).
State Bank of India Leaks Customer PII
Last week, a new account with the name “Siriusim” published a post to the mainstream data breach website BreachForums. They had new user data from SBI, they claimed, including personal user information, new account and loan applications, and more. The data included a table with 375,000 rows, and 2,722 PDF files. Importantly, neither figure necessarily indicated the total number of individuals impacted.
As part of the post, Siriusim featured a few documents with handwritten personal information. Mumbai’s Free Press Journal verified that PII from the breach samples was valid, belonging to real Indian citizens. One individual, for example, lost their mobile number and know your customer (KYC) documentation in the breach, and the WhatsApp photograph associated with their number matched the passport photo included in the KYC file.
SBI acknowledged that leaked data included names, genders, mobile numbers, email addresses, home addresses, dates of birth, bank profile IDs, metadata associated with loans, and “other files.” Follow-on reporting out of Mumbai suggested that this extra data included Central KYC numbers — a single identifier for financial accounts in India — and video KYC verification data, and the kinds of files one might have to submit in the process of creating a new bank account, or filing for a loan. For instance, one published document included an individual’s employment and income declaration, with details about their current employer, work experience, and salary.
Exactly what precipitated the leak, and why it affected only 0.0008% of the bank’s customers, remains unclear. In its formal declaration, SBI emphasized that “the bank’s core business functions continue to operate normally without disruptions.” Altogether, these clues might point to a breach of some peripheral digital service or data-handling system, rather than the core bank system.
In fact, SBI’s last major customer data leak followed just such a script. In 2019, it exposed customer account data through a single server at a Mumbai data center, which was missing password protection. The server supported its “SBI Quick” system, used to text and call customers about basic account information. That one machine put millions of customers at risk, perhaps highlighting just how minor this new leak really is.
Deeper, Less Obvious Cyber-Risks From Banking Breach
“If the data is genuine, the main risk is not direct account theft but credible-sounding phishing, vishing, and identity or loan fraud, since attackers who know someone’s details can impersonate the bank convincingly,” explains independent security researcher Sushant Bhardwaj.
Email addresses, phone numbers, and dates of birth carry fairly obvious risk in the hands of bad actors, and less common kinds of PII can add color to otherwise generic identity attacks. For instance, “KYC details are hard to change, so they can support identity fraud, such as applying for credit in someone else’s name or answering account-verification questions,” Bhardwaj notes. And with regard to loan metadata, “a caller who can quote real loan details can pose as the bank or a recovery agent and pressure a borrower into paying a ‘fee’ or sharing a one-time password (OTP).”
Brian Hussey, senior vice president for Cyderes’ Howler Cell, goes deeper. Last month, his team reported on an Indian data broker selling personal records for only about 5 rupees (6 cents or so) per lookup, through a Telegram bot and business application programming interface (API) platform. Using these simple lookups, cybercriminals targeting Indian citizens can obtain vast stores of PII belonging to regular citizens in an instant. And data breaches like SBI’s, Hussey notes, can feed into this underground economy. “A breach dump goes stale the day it’s posted. A live lookup service is always current, because it is asking the authoritative source in real time. India’s underground data market has both, and they work together,” he explains.
Say, for example, that an individual applied for a sizable loan from SBI — indicating that they might be a valuable person to target — and some information about them and their application leaked last week. “In India we have documented services that turn [data such as] a mobile number into a subscriber identity, an employment history, and a list of registered vehicles,” Hussey says. Not only can an attacker turn a little bit of PII into a lot, but the vast, fluid economy for this sort of stolen data makes recourse for victims near impossible. Hussey notes that such a query might only cost a few seconds, and “leaves no intrusion, no anomaly in the provider’s logs, and no accountable buyer. You cannot investigate an event that never registers as one.”
“India built one of the most connected identity systems in the world, and an entire industry exists to query it,” he warns. “That connectivity is what makes a leak in one place so impactful and useful somewhere else.”
Read more about: