PHP2Shell Attacks Root Palo Alto Firewalls but Fail Against WordPress
Over 22.6 million exposed instances are potentially affected by the critical PHP flaws that have been targeted for over a week.
Stay up to date with the latest cyber security news and threats from around the world.
Over 22.6 million exposed instances are potentially affected by the critical PHP flaws that have been targeted for over a week.
Noteworthy stories that might have slipped under the radar: Iran eyed in military freezer hacks, Copenhagen University breach, AI-powered malware.
As organizations eliminate passwords, attackers will adapt. Instead of attacking the authenticator directly, they will look for opportunities around it.
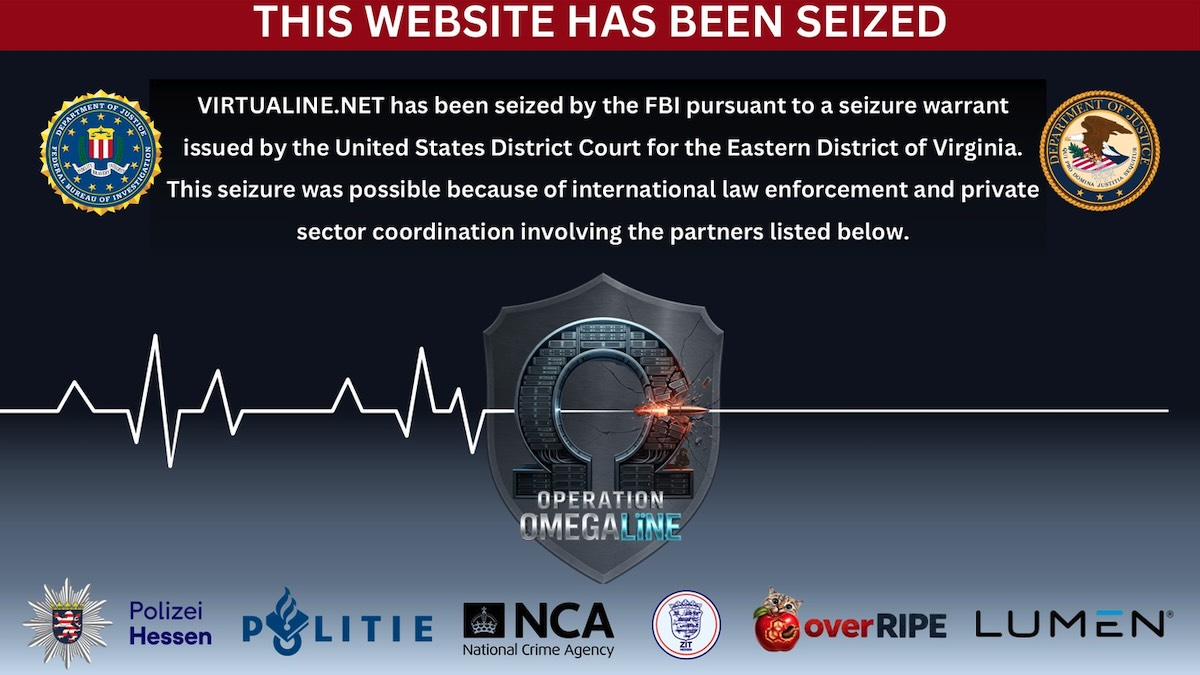
It allowed customers to host hack-for-hire services, supported ransomware and infostealer operators, and accepted crypto payments.
Threat actors are attempting to exploit a high-severity unauthenticated race condition leading to remote code execution.
Malicious code linked to a website monitoring tool was designed to hijack logged-in Polymarket sessions and siphon user funds.
Tracked as CVE-2026-97229, the bug allows unauthenticated attackers to execute arbitrary code on the server.
An integer overflow tracked as CVE-2026-111585 could be used to execute arbitrary code on the viewer’s system.
Risk managers are trained to spot weak signals, plan for disruption and make hard decisions under uncertainty. But the discipline looks different when the risk is not a...
Google’s new frontier model scored 88.2% on SEC-bench Pro and is rolling out first to vetted cyber defenders via its Fairwind Program.
Unpatched voting machines, unverifiable QR-coded ballots, and AI-driven influence campaigns leave US elections short of secure.
Cisco open sourced Project Quarry, a rule language for detecting AI agent attacks that only emerge across sequences of benign actions.
The flaws could lead to arbitrary code execution, authorization bypasses, and privilege escalation.
Hackers stole personal information and iRhythm account and device data from third-party-hosted business applications.
CVE-2026-41709 allows attackers with administrative privileges to perform operations without being logged.
The massive funding round comes just days after reports emerged that Upwind had attracted acquisition interest from several companies, including Datadog
The Chrome 156 update fixes 52 bugs, while Firefox 159 was rolled out with 167 security patches.
FoxIO disclosed three GoAhead TLS bugs that can let revoked certificates through or expose some encrypted sessions to eavesdroppers.
The attackers chained PHP2Shell and Fragnesia exploits and hacked two servers of a US government-affiliated organization.
Four EPICS Base flaws found by an autonomous system could let attackers crash processes at particle accelerators and fusion labs.
The process that gates nearly every B2B deal is a self-assessment the sender distrusts and the receiver accepts. There is finally a better basis for trust between companies.
The company will use the Series B funds to expand its platform for securing AI agents’ access to sensitive systems.
CVE-2026-101767 is an unauthenticated SQL injection that can be exploited for remote code execution.
Tailscale is preparing a patch for Tailscale SSH flaws whose details went public over the weekend, before any fixes had been released.