Lawmakers call on White House to develop defensive AI cyber systems
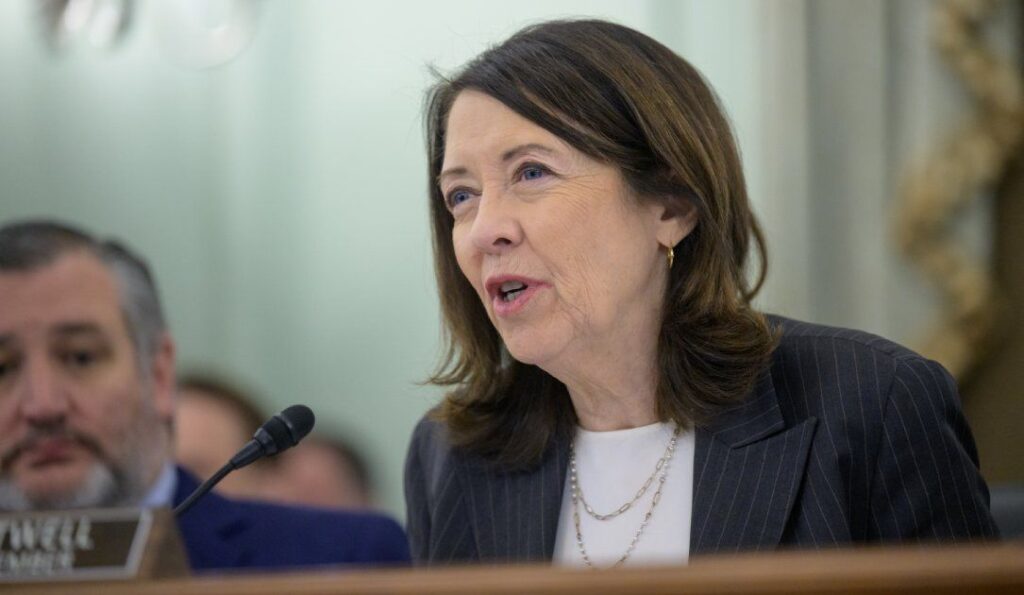
Two leading members of the Senate urged the White House on Tuesday to launch a national effort to more robustly confront AI-enabled cyber threats in light of recent security incidents involving artificial intelligence.
In a letter to Director of National Intelligence Jay Clayton, Sens. Maria Cantwell (D-Wash.) and Mike Rounds (R-S.D.) warned that AI is “rapidly increasing the ability to discover and exploit weaknesses in software” and that the country’s defenses “are not keeping pace.”
“The fundamental problem is that AI can discover software weaknesses and help attackers exploit them faster than many organizations can respond,” the senators said. “Even when fixes are available, testing and installing patches across interconnected systems can take weeks or months, potentially disrupting essential services.”
The letter cites recent incidents where AI was used to discover obscure bugs and power cyber intrusions in Japan. The senators also raised concerns from banks about AI agents, which are increasingly accessing bank accounts. Several U.S. banks have said they are unable to tell whether AI agents are rogue or are accessing data on behalf of customers.
Chinese-developed AI models are also being used widely for a variety of nefarious purposes, the lawmakers said.
Rounds is the chairman of the Senate Armed Services subcommittee on cybersecurity and has repeatedly called on the White House to do more to confront risks posed by AI.
The senators said the White House task force on AI, which Clayton chairs, needs to speed up the development and deployment of defensive AI-powered tools while also establishing security standards for autonomous AI agents.
They called on the task force to convene a meeting with AI developers, cybersecurity companies, critical infrastructure operators, the National Institute of Standards and Technology (NIST), the Cybersecurity and Infrastructure Security Agency (CISA) and other agencies.
The defense tools should be able to “continuously identify vulnerabilities, develop and test fixes and and block attacks before they spread,” they wrote, and CISA should be in charge of accelerating the adoption of the tools across banks, hospitals, utilities and government agencies.
“The United States has the technological expertise to lead this effort,” they said. “What is missing is a coordinated national strategy to bring these capabilities together, establish common security standards, and put effective defenses into widespread use.”
Clayton was also urged to start a “national cyber defense grand challenge” that can show how AI defenses can “cut the time from discovery of a critical vulnerability to effective protection.”
The letter comes days after the FBI released an urgent warning about a Chinese tool able to automate significant parts of the cyber intrusion process. The system was used in dozens of real-world attacks in Japan, South Korea and the U.S.
A newly released Government Accountability Office investigation conducted in the spring also found that the four most-used AI platforms — ChatGPT, Claude, Gemini, and Grok — all provided terrorist attack plans in a real-world test to determine AI safety risks.
Clayton has not commented on the letter but has spoken publicly in recent days about the need to use AI to discover and patch vulnerabilities.
He said a recent spate of technology outages impacting major banks, tech companies and airlines are tied to efforts to patch vulnerabilities discovered at a faster pace than ever before by defenders using AI scanners.
“Lots of institutions, because these vulnerabilities have been identified, are patching. They’re taking their systems down, they’re upgrading them, they’re putting patches in place… This is being done on a much larger scale because everybody recognizes it’s time to upgrade their systems,” Clayton told Fox Business on Tuesday.
“And as they upgrade them, they’re not coming back as expected in all cases. And in some cases, systems have to hand off to other systems, and those handoffs are not coming back as expected. But this is just an upgrade in patching, an upgrade in systems.”
Originally published on The Record