Container Store restores systems after cyberattack
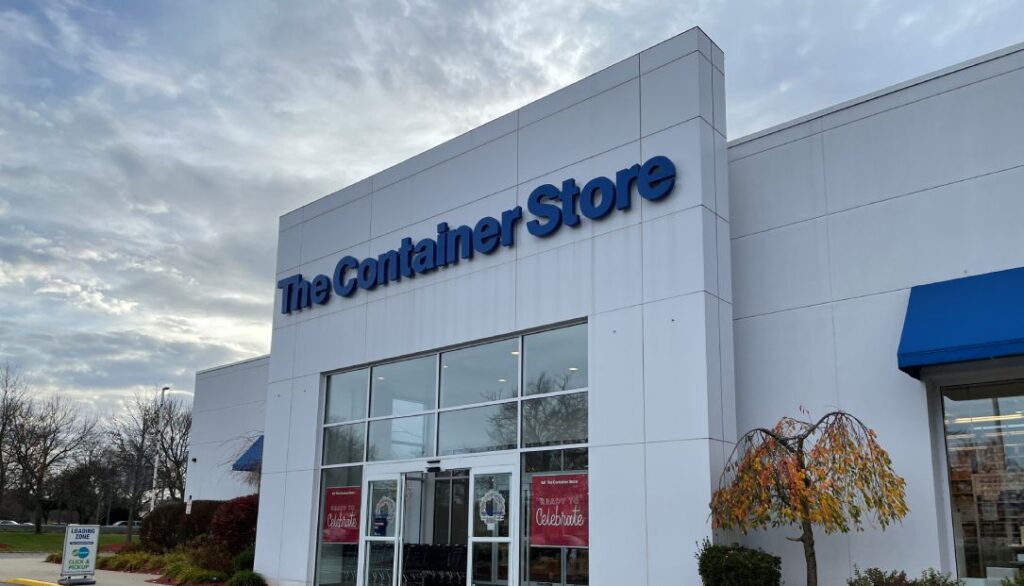
The Container Store on Friday said it is recovering from a cyberattack that forced it to shut down its online ordering systems and limited in-store transaction processing.
The firm’s parent company, Neighborhood Intelligence, said in a statement that The Container Store has “restored its website and systems following a cybersecurity incident this past weekend.” Neighborhood Intelligence — a rebrand of Bed Bath & Beyond — purchased The Container Store in July for $150 million.
While the stores remained open throughout the week, they had to use “alternative transaction-processing procedures,” according to the statement. The Texas-founded company has about 100 stores across the U.S.
Neighborhood Intelligence said the incident only impacted The Container Store and did not affect its other brands including Bed Bath & Beyond, Overstock, buybuy BABY or Kirkland’s. Neighborhood Intelligence reported $509 million in revenue for the third quarter earlier this month, with the increases driven primarily by the acquisition of The Container Store.
The company said it hired cybersecurity experts to contain the incident and restore the affected systems. So far, it does not appear the hackers stole customer financial data, but did not address claims made by the cybercriminal group n0n, which listed the company on its leak site earlier this month.
The n0n cybercriminal group emerged in September, and cybersecurity experts say they specialize in ransomware and data extortion. The group has attacked more than 100 victim organizations and demanded hundreds of millions of dollars in ransoms.
The group initially forced victims to pay a 10% fee just to access its negotiation portal, but now forces companies to pay the full ransom before viewing any sample of the stolen information, according to SOCradar.
Allan Liska, a ransomware expert at Recorded Future, said the group launched its data leak site in late September and tried to recruit affiliates on a Russian cybercrime forum called RehubcomPro Forum in late October.
Liska said the group’s cybercriminal post claimed affiliates were instructed to only target companies that earn more than $10 million annually in revenue and were banned from attacking organizations in the Commonwealth of Independent States. The Record is an independent unit of Recorded Future.
Cybersecurity firm LevelBlue said the group has primarily targeted healthcare and pharmaceuticals but recently claimed to have troves of data from financial services companies and retail firms.
LevelBlue noted that the group has used an AI coding agent and paid AI services to write and debug its attack scripts, helping it scale operations quickly.
Originally published on The Record