European Commission confirms cyberattack, says hackers used AI tool
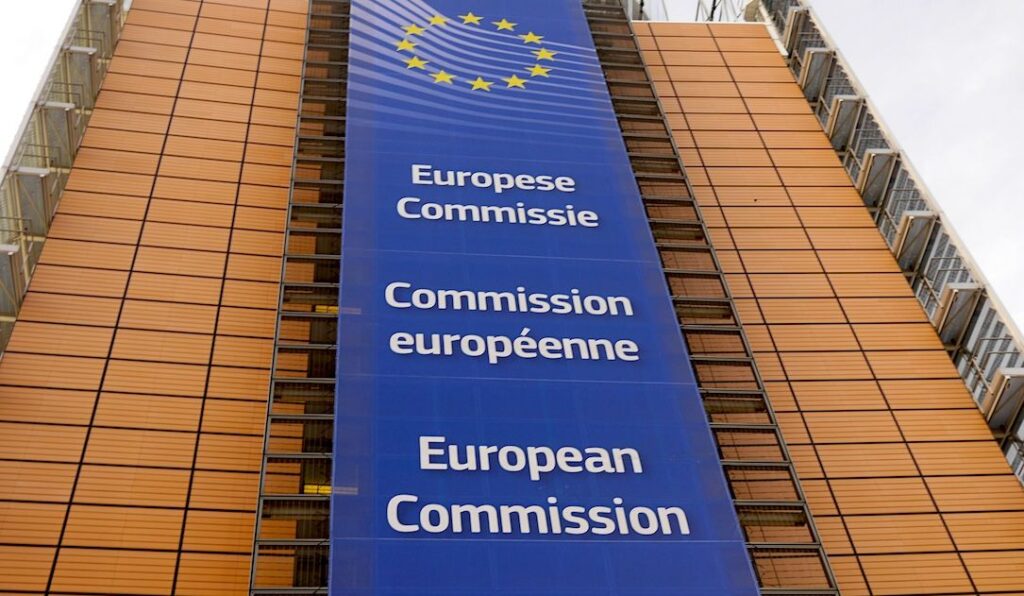
The European Commission confirmed Thursday that it had been hit by a cyberattack last month involving a publicly available artificial intelligence tool, following media reports of the incident.
Speaking to journalists, Commission spokesperson Thomas Regnier said the first signs of the attack were detected October 22. He described the incident as an “AI-generated cyber campaign” but did not identify the tool used or the attackers’ apparent motivation.
POLITICO first reported that the Commission had been impacted by the cyberattack. It said CERT-EU had identified the attackers’ use of ARTEX, an open-source AI hacking platform that the FBI last week warned was being used both by criminals and state-sponsored groups.
The attack reportedly disrupted the European Commission’s personnel systems for more than 10 days, including payroll, leave requests, medical reimbursements and translation services.
A commission spokesperson confirmed to Recorded Future News they had “taken the necessary steps in response to a detected cyber campaign,” including taking several services offline as “a protective measure.”
They said they had notified affected individuals and were “preventively checking other systems” while keeping in touch with CERT-EU and the European Data Protection Supervisor.
Regnier said investigators had found no evidence of a data breach affecting Commission staff broadly and were unaware of any ransom demand. He said the investigation remains open.
Asked why the incident was not disclosed earlier, Regnier said publicizing defensive measures could undermine their effectiveness. “There was no hiding whatsoever,” he told journalists.
The incident follows an alert issued in June by the Five Eyes intelligence alliance, which said AI would fundamentally transform both offensive and defensive cyber capabilities. “The timeline is not years, it is months,” it said at the time.
The FBI warned last week that ARTEX was being used prolifically by cybercriminals and nation-states to breach government agencies and dozens of critical sectors worldwide, “with some intrusions progressing from initial targeting to privileged access in under three hours.”
The open-source framework, which was released in July, uses commercial AI models to automate vulnerability discovery and exploitation.
“The key takeaway here is not that threat actors are using Artex,” said Shaun Williams, a senior director at SentinelOne, “but that the widespread availability of AI-powered tools like Artex have allowed threat actors to find and exploit vulnerabilities in internet facing devices faster, more effectively, cheaper, and with less skill than ever before.”
The attack is the Commission’s third disclosed cyber incident this year, following breaches involving Ivanti software in January and its cloud infrastructure in March. Officials have not linked the incidents.

Alexander Martin
is the UK Editor for Recorded Future News. He was previously a technology reporter for Sky News and a fellow at the European Cyber Conflict Research Initiative, now Virtual Routes. He can be reached securely using Signal on: AlexanderMartin.79
Originally published on The Record