Why Caribbean Threats Cascade Into Global Cyber-Risk
The region is demonstrating what happens when exploits accelerate but assurance does not.
COMMENTARY
The region is demonstrating what happens when exploits accelerate but assurance does not.
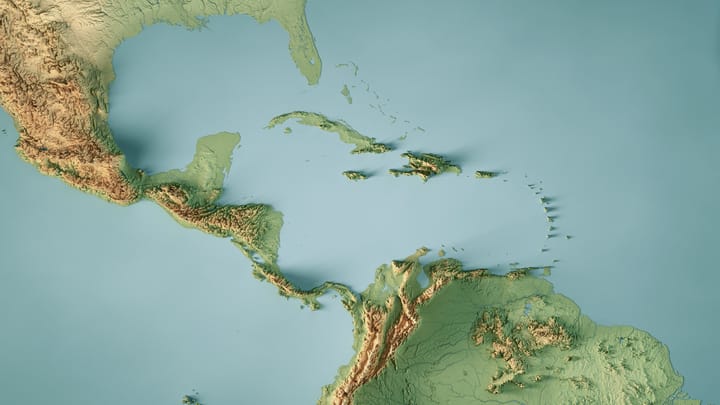
On July 24, 2025, Curaçao’s Tax and Customs Administration found ransomware on its network. Counter services, the call center, and internal processes went dark for more than a week, and the island’s recovery depended on specialists flown in from the Netherlands.
A day earlier, the Joint Court of Justice had gone down as well. Because that court serves Curaçao, Aruba, Sint Maarten, Bonaire, Saba, and Sint Eustatius, a single intrusion degraded the judicial system of six jurisdictions at once.
One platform, six governments.
That is the Caribbean’s defining security characteristic, and it is why the interval between an exposure appearing and an exposure closing matters more here than almost anywhere else.
The Speed Gap
Consider what that interval currently is.
Fortinet’s “Global Threat Intelligence Report: 2026 Midyear Edition” recorded roughly 325 million attack attempts across the English-speaking Caribbean in 2025, an extraordinary volume against a small economic base, with critical vulnerabilities now targeted within 24 to 48 hours of disclosure, down from an average of nearly five days.
IBM’s 2026 “Cost of a Data Breach Report” puts the mean time to identify and contain a breach at 247 days, up 2.5% and reversing five consecutive years of improvement.
Both of those numbers moved this year, and they moved in opposite directions. Exploitation got faster. Finding and containing it got slower, for the first time in five years.
When Assurance Falls Behind
Here is the part that the security industry has not absorbed: third-party assurance still runs on an annual cycle. A global insurer assesses its Caribbean claims processor once a year.
A hotel chain reviews its regional franchisee’s controls at renewal. A correspondent bank collects an attestation and files it. Every one of those instruments is calibrated to a threat landscape that stopped existing several years ago.
The questionnaire signed in March describes a network that was materially different by April and unrecognizable by October. Twelve months of assurance against 48 hours of exposure, and nobody has repriced the difference.
Global Issue
That mismatch is not a Caribbean failing. It is a global control design failing, and the Caribbean is simply where it shows up first because of what sits inside the interval.
The plumbing is ordinary. A business process outsourcer holds live credentials into a North American insurer’s claims platform. A hotel group’s property management system federates to a global loyalty program. A regional bank sits inside correspondent rails that clear in New York. An attacker who compromises the small end inherits trust at the large end, and does it inside a window where the large end’s assurance process has no way to notice.
The obvious response is that Caribbean organizations should simply patch faster.
Having spent two decades running security operations across these markets, I can tell you why that answer keeps failing. Security teams here are frequently two or three people covering an entire institution.
Critical systems often cannot be taken offline because there is no redundant capacity to fail over to. Vendor support is remote and time-zoned away. And where six jurisdictions share one platform, no single institution can authorize a maintenance window on it.
These are structural constraints, not attitudes, and telling the region to try harder has not moved the number in years.
Measure remediation against exploit velocity, not the audit calendar. Report critical MTTR as a distribution against a 48-hour benchmark. An average conceals the tail, and the tail is where the exposure lives.
Replace annual attestations with continuous evidence. If your assurance over a supplier is a document signed in March, you are not managing that risk; you’re recording that you once looked at it.
Assume some things can’t be patched in time, and design for that. Segmentation, compensating controls, and explicit, owned, time-boxed decisions about what stays exposed. An undocumented exception is the same as no control.
Instrument the federated paths, not just the perimeter. Stolen credentials remain the primary route into cloud environments, and federated access is where a stolen credential stops being your incident and becomes your partner’s.
Assess the shared provider, not just the institution. Where multiple entities run on one platform, assessing each separately measures the same risk repeatedly and reduces it once, at best.
The Caribbean isn’t asking for allowances. It is showing the rest of the industry, early and in public, what happens when exploitation accelerates and assurance does not.
Anyone whose supply chain touches this region is measuring a snapshot of a system that has already changed.